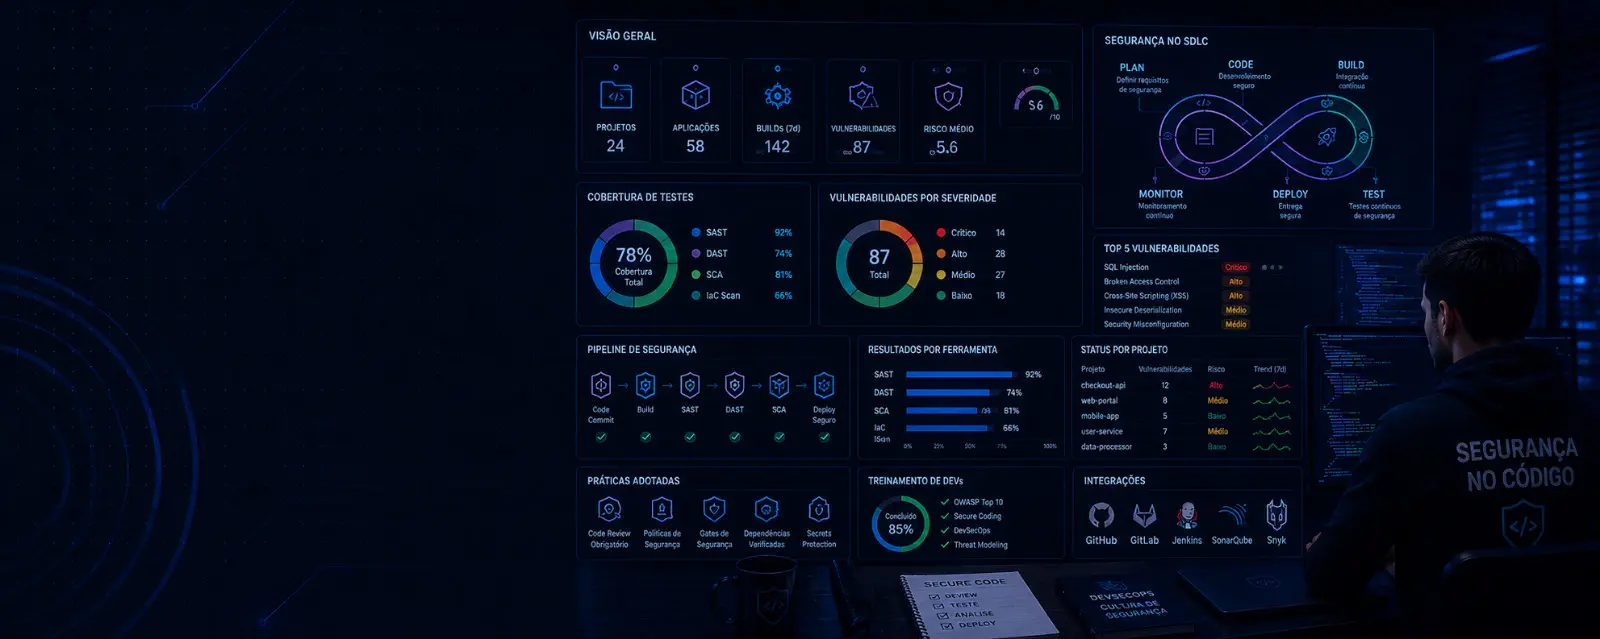
Security integrated into the development lifecycle
Security integrated into development from the first commit.
Continuous integration of security practices into the development lifecycle, including code analysis, dependency validation, test automation, and technical team enablement.
Security integrated into the engineering workflow.
Mapping of the development lifecycle, technologies used, and risks present in the current pipeline.
Definition of SAST, DAST, SCA, and secrets scanning solutions most suitable for the organization's technical context.
Implementation of automated controls in the pipeline for preventive blocking of critical vulnerabilities.
Specialized code review focused on critical vulnerabilities, business logic, and secure development practices.
Practical secure coding enablement based on the technology stack and real risks of the environment.
Continuous tracking of security maturity with operational metrics and evolutionary indicators.
Technical and operational results for continuous AppSec maturity evolution.
Engineering profiles and technical leadership where security and velocity must coexist.
Teams that want to incorporate security into the workflow without compromising productivity and velocity.
Technical leaders who need to reduce operational risk and increase engineering maturity.
Organizations developing software continuously that need to ensure security at scale.
Talk to our specialists and discover how to integrate security into the development lifecycle in a practical, scalable way aligned with your business.